Blogs
Latest Insights on Governance, Risk & Compliance Across the GCC

Optimizing Existing Compliance Programs with GRC Automation: How to Move from Manual Compliance to a GRC Platform
ISO 27001
SAMA CSF
SOC 2
GRC Fundamentals

How Long Does ISO 27001 Certification Take With and Without Automation?
ISO 27001
Frameworks
Optimizing Existing Compliance Programs with GRC Automation: How to Move from Manual Compliance to a GRC Platform
ISO 27001
SAMA CSF
SOC 2
GRC Fundamentals

What Founders Need to Know Before Starting Compliance
GRC Fundamentals
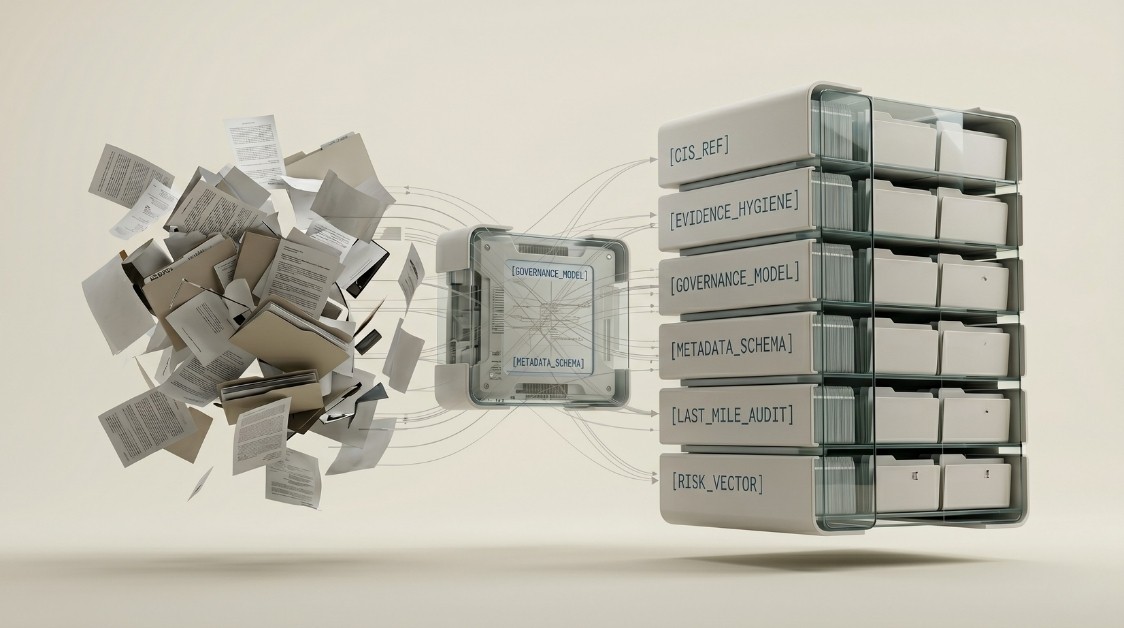
Optimizing the Unavoidable: Advanced Frameworks for Manual Evidence
Frameworks
GRC Fundamentals

Local vs. Global: Why US-Based GRC Tools Often Fall Short on Middle Eastern Regulatory Frameworks
ISO 27001
SAMA CSF
SOC 2
How Long Does ISO 27001 Certification Take With and Without Automation?
ISO 27001
Frameworks
Advanced CISO Guide to ISO 27001 in Middle East FinTech: Beyond the Audit
ISO 27001
Frameworks
Optimizing Existing Compliance Programs with GRC Automation: How to Move from Manual Compliance to a GRC Platform
ISO 27001
SAMA CSF
SOC 2
GRC Fundamentals
How Long Does ISO 27001 Certification Take With and Without Automation?
ISO 27001
Frameworks
Optimizing Existing Compliance Programs with GRC Automation: How to Move from Manual Compliance to a GRC Platform
ISO 27001
SAMA CSF
SOC 2
GRC Fundamentals
Local vs. Global: Why US-Based GRC Tools Often Fall Short on Middle Eastern Regulatory Frameworks
ISO 27001
SAMA CSF
SOC 2
What Founders Need to Know Before Starting Compliance
GRC Fundamentals
How Long Does ISO 27001 Certification Take With and Without Automation?
ISO 27001
Frameworks
Optimizing the Unavoidable: Advanced Frameworks for Manual Evidence
Frameworks
GRC Fundamentals
Advanced CISO Guide to ISO 27001 in Middle East FinTech: Beyond the Audit
ISO 27001
Frameworks